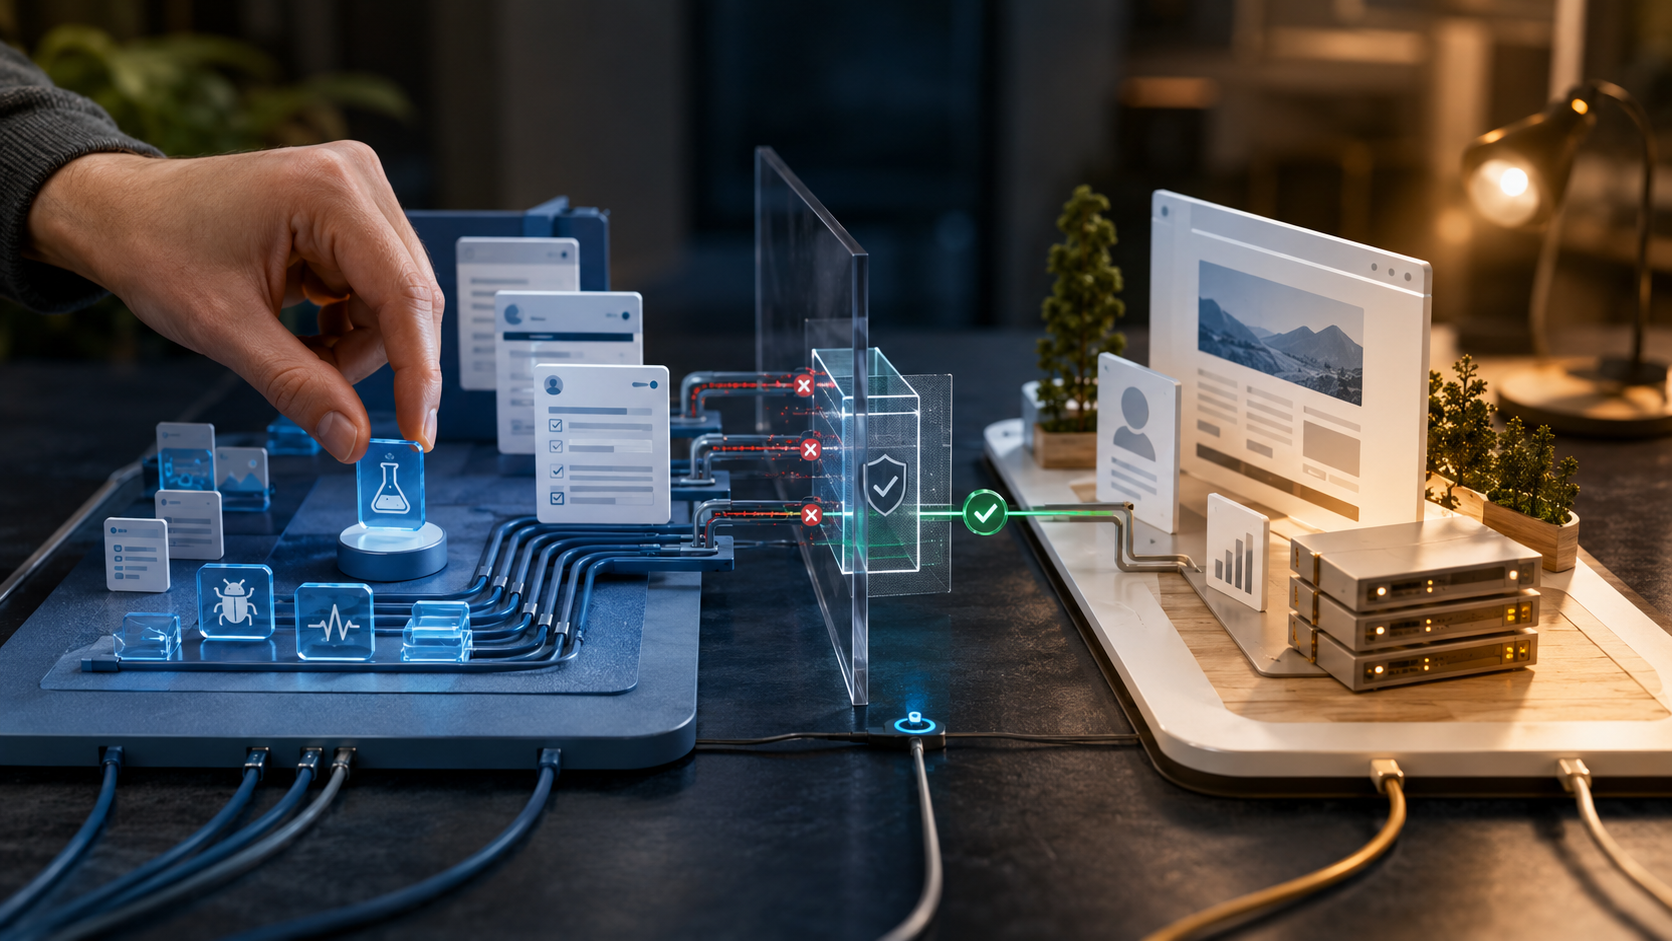
A staging site is supposed to make testing safer. But if its forms still send to the live CRM, its webhooks still call production endpoints, or its analytics still mix test activity into the real property, the staging environment becomes another way to damage production data.
The fix is not simply “remember to use fake names.” A reliable staging setup gives each environment its own destinations, credentials, tracking rules, and test data policy. It also proves those boundaries with deliberate tests before anyone clicks through a form.
Staging is a different environment, not a second copy of production
Teams often think of staging as a visual copy of the live WordPress site. That is useful for reviewing pages, but it is incomplete. A website is also a set of connections:
- Forms send notifications and create records.
- Webhooks call external APIs.
- Marketing platforms receive subscribers or events.
- Analytics tools collect page views and conversions.
- Payment, search, personalization, and support tools may be embedded in the page.
Copying the code and content without reviewing those connections can preserve the wrong behavior. A staging form may look correct while quietly creating a real contact, sending an email to a customer, or registering a conversion against a live campaign.
Start with an environment map
Before changing a form or integration, write down what each environment is allowed to touch. The map does not need to be complicated. It should answer five questions for every connection:
- What starts the action, such as a form submit, scheduled job, or page view?
- Where does the data go?
- Which credentials authorize the request?
- What kind of data is allowed to cross the boundary?
- How will the team know that the test succeeded or failed?
For example, production may send a lead to the live CRM, while staging sends the same field structure to a sandbox account or a dedicated test list. Production analytics may use the primary measurement property, while staging uses a separate property or a clearly filtered test stream. If a vendor has no sandbox, the fallback might be a mock endpoint, a disabled action, or a review-only capture that never leaves WordPress.
Record the decision in configuration documentation, not only in one developer’s memory. Environment variables, deployment settings, and integration notes should agree about the destination.
Forms need a safe submission path
Forms are the most visible source of staging mistakes because the button is easy to test and the side effects happen elsewhere. A staging form can have the correct labels and validation while still using production notification addresses, CRM credentials, autoresponders, or hidden campaign fields.
Use a test submission plan that names the allowed recipient, record destination, identifier, and cleanup step. A good test record is obviously synthetic, such as staging-test-2026-08-24@example.invalid, and it should never resemble a real constituent or customer. Do not use real personal information just because it is convenient.
Check every action attached to the form:
- Confirmation messages and redirect URLs.
- Internal notification recipients.
- CRM or database storage.
- Webhooks and API requests.
- Email automation enrollment.
- Analytics events and conversion names.
If staging must exercise the full workflow, route the data to dedicated test records or a sandbox. If the external system cannot isolate test data, make the action observable and reversible, or disable it and test the request with a mock service instead.
Webhooks require destination and credential separation
A webhook URL is not just a label. It identifies a destination, and the credentials or signing secret often determine which account receives the request. Changing the WordPress site URL does not change a webhook target.
Keep staging and production webhook endpoints separate whenever the receiving platform supports it. Use separate secrets and tokens, too. If the same secret works in both environments, a configuration mistake can be difficult to detect and harder to contain.
Test more than the HTTP response. Capture the request timestamp, endpoint, event name, test identifier, response status, and downstream record ID when one exists. A response of 200 tells you that the receiver accepted the request at the protocol level. It does not prove that the record landed in the intended account, matched the intended test record, or triggered the correct follow-up.
Keep analytics test activity out of the reporting property
Staging pages can contaminate analytics in quieter ways. A developer may browse several pages, submit a form repeatedly, or trigger a conversion event while debugging. Those events can look like real traffic if staging uses the same measurement destination and there is no reliable way to identify the environment.
The cleanest approach is a separate staging property or data stream. If that is not practical, use an explicit environment signal and confirm that reports, audiences, and downstream exports exclude it. Do not assume that a hostname filter alone is enough. Validate the event payload, page location, measurement destination, and reporting behavior together.
Consent behavior also needs a staging test. A test environment should not hide problems in denied-consent paths or make every event appear because a developer has browser extensions and administrative access that normal visitors do not.
Common boundary failures
Several mistakes appear repeatedly:
- A database refresh copies production form settings into staging after the staging configuration was corrected.
- A deployment replaces environment-specific values with defaults from a local configuration file.
- A plugin stores an endpoint or credential in the database, outside the deployment variables the team reviews.
- A staging page includes production marketing scripts because the template was copied without an environment check.
- A test uses a real email address, and an automation journey treats it as a genuine new subscriber.
- A team validates the form response but never checks the destination system.
These are configuration and process problems, not just WordPress problems. The solution is to make environment-specific behavior visible, reviewable, and testable.
Use a pre-launch boundary test
Before a staging build is approved, run a short acceptance test with a known synthetic identifier:
- Open the form from the staging hostname and confirm that the page identifies the test environment where appropriate.
- Submit one valid record and one invalid record.
- Confirm the expected confirmation and notification behavior.
- Inspect the request or log for the endpoint, event name, environment marker, and response.
- Verify the record exists only in the approved test destination.
- Confirm that no production CRM record, marketing enrollment, customer email, or live conversion was created.
- Repeat the test after deployment and after any database or content refresh.
- Remove or label test records so they cannot be mistaken for real activity.
Keep evidence for the test, including the timestamp, build or release identifier, test value, destination, and result. That evidence turns “we tested it” into something another person can review.
Make the safe path the easy path
Teams should not have to remember every destination on every release. Store environment-specific values in a controlled configuration layer, use separate credentials, make dangerous production targets difficult to select from staging, and add a visible warning or environment indicator to test sites. Add automated checks where possible, such as failing a deployment when a staging build contains a known production endpoint.
Also give the workflow an owner. Someone should be responsible for the environment map, test data policy, and boundary checks when a form, plugin, integration, or analytics tag changes.
Protecting production starts before launch
A staging site is trustworthy when its boundaries are intentional and proven. Forms should have safe destinations, webhooks should use separate endpoints and credentials, analytics should isolate or identify test activity, and every test should verify the downstream result instead of stopping at the submit button.
DigitalWerks can review a WordPress staging setup, map its form and integration destinations, and build a repeatable acceptance test for the paths that matter. Talk with DigitalWerks about making your next website test safer to run and easier to verify.