A website form can be technically available and still be operationally unusable when spam fills the inbox, pollutes the CRM, and hides legitimate requests. The answer is rarely a single CAPTCHA. Reliable form protection combines lightweight bot signals, server-side limits, clear user feedback, moderation paths, and checks that confirm real submissions still reach the right destination.
This guide explains how to design that layered workflow. The examples apply to contact forms, quote requests, registrations, feedback forms, and donation or volunteer inquiries. The goal is not to identify every automated request perfectly. The goal is to reduce obvious abuse, slow repeated attacks, preserve accessibility, and keep uncertain records reviewable instead of silently discarding them.
Start with the submission workflow, not the anti-spam tool
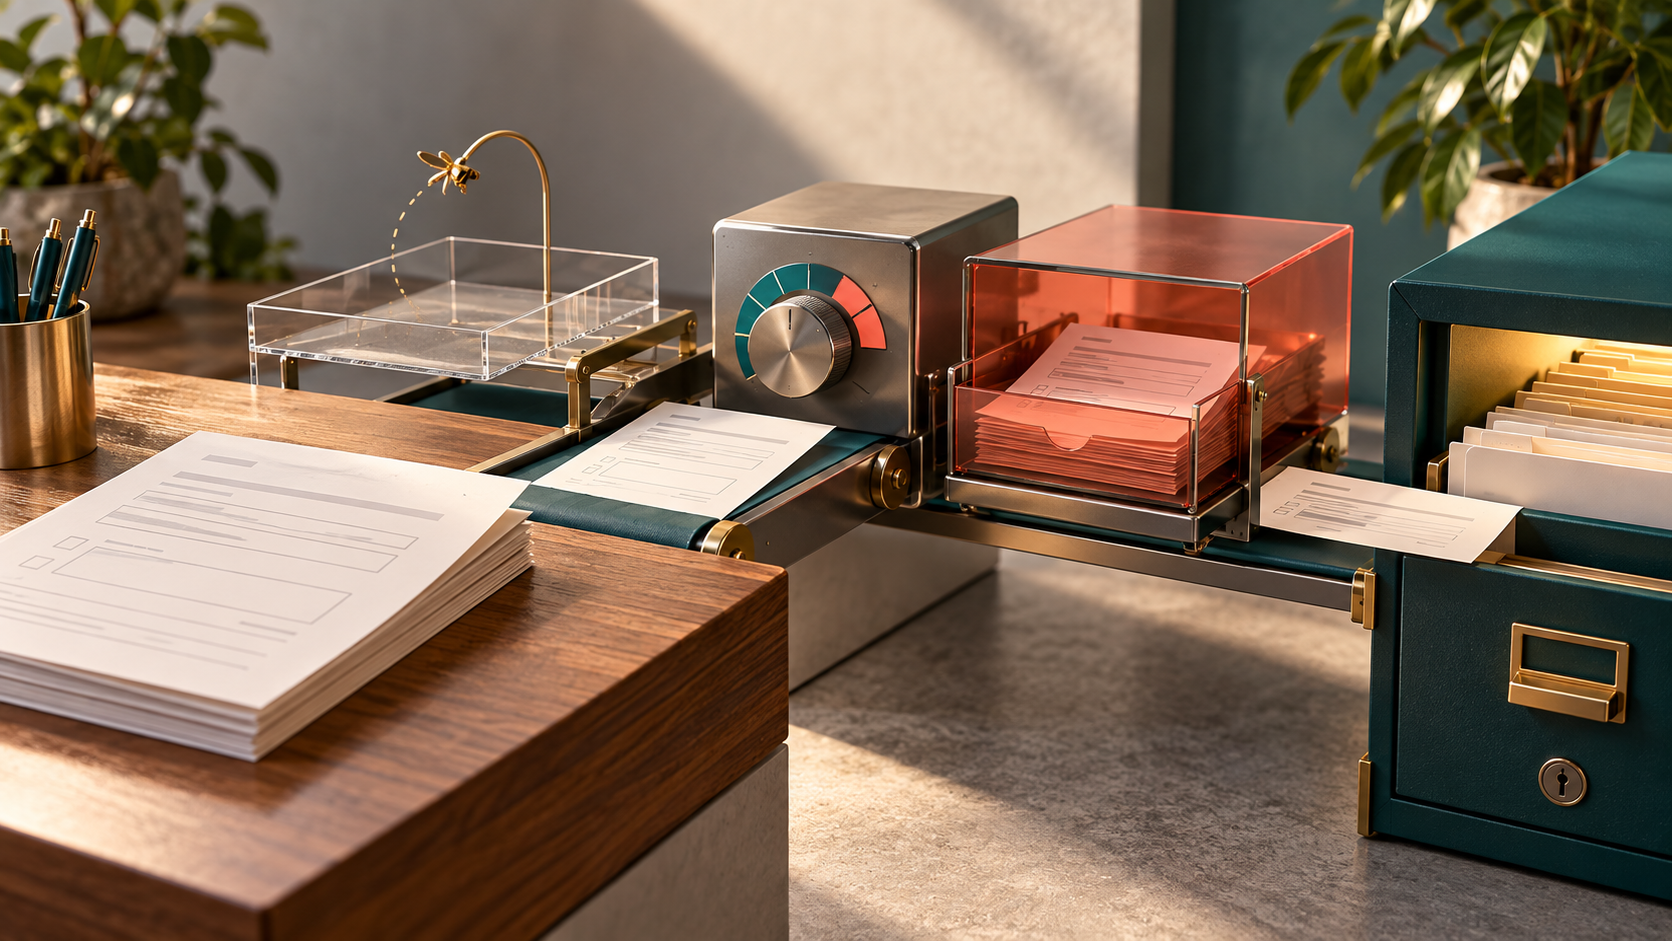
Before choosing a plugin or service, map what happens after someone presses Submit:
- The browser sends the form fields and any security tokens.
- The application validates required fields, formats, permissions, and request freshness.
- Bot and abuse signals are evaluated.
- The submission is accepted, rejected, throttled, or held for review.
- Accepted data is stored and sent to notifications, a CRM, an email platform, analytics, or another API.
- Operations staff see the outcome, including failures and items waiting for review.
This map matters because spam prevention can fail in two opposite ways. A weak control lets abusive traffic through. An aggressive control blocks a real person, while the team sees no trace of the lost request. A useful design makes each decision visible enough to troubleshoot without exposing sensitive data.
DigitalWerks recommends treating the form as a small data pipeline. The same approach used in a broader website form acceptance test applies here: test the user experience, the stored record, the downstream handoffs, and the failure path together.
Use cheap signals before expensive challenges
Most sites should begin with controls that do not interrupt a legitimate visitor.
1. Validate the request on the server
Browser-side checks improve the experience, but they are not a security boundary. A visitor or bot can bypass JavaScript and send a request directly to the endpoint. Repeat the important checks on the server, including allowed field names, required values, maximum lengths, expected formats, and any workflow-specific rules.
Do not treat an email address that passes a format check as proof that the request is legitimate. Validation answers whether a value is shaped correctly. Abuse detection answers whether the request should be trusted, slowed down, or reviewed.
2. Add a honeypot carefully
A honeypot is an extra field that real visitors should not complete, often because it is hidden from ordinary users while remaining available to simple bots. If the field contains a value, the server can reject or quarantine the submission.
Honeypots are inexpensive, but they are not universal protection. Some bots understand common field patterns, and poorly implemented hidden fields can be exposed to screen-reader or keyboard users. The field should be removed from the normal interaction path, labeled appropriately if it remains discoverable, and tested with assistive technology. A honeypot is one signal in a layered system, not a reason to skip server-side validation.
3. Track timing and request volume
Record enough metadata to identify rapid repeated submissions, such as a short-lived session or request token, a timestamp, and a privacy-reviewed network signal. A form completed in an impossible interval may deserve extra scrutiny. A burst of requests from the same source may need throttling.
Keep the rule proportional. A short form may be completed quickly by a real person. A long form may take much longer. Use timing as one input, set a reasonable threshold, and provide a recovery path when a legitimate request is challenged.
Rate limits should protect the endpoint and the downstream systems. Limit requests per IP or session where appropriate, but also consider shared networks, mobile carriers, accessibility tools, and organizational offices. A limit that is too narrow can block an entire workplace or library. Log the decision category, not the full submission content.
Decide what happens to uncertain submissions
A binary pass-or-fail rule is often too blunt for a valuable contact or registration form. Use at least three outcomes:
- Accept: the request passes validation and abuse checks, so it can continue to storage and downstream delivery.
- Review: the request is plausible but has a signal that needs human judgment. Store it with a review status and prevent automatic follow-up until someone approves it.
- Reject or throttle: the request clearly violates a rule or exceeds a limit. Return a useful response without revealing which detection rule fired.
The review path needs ownership. Define who checks it, how long items remain available, what evidence they can see, and what happens after approval. If quarantined submissions disappear into a log that nobody monitors, the system has simply moved the failure out of sight.
For sensitive forms, minimize what is retained in abuse logs. Store a reference to the submission and a short reason code rather than copying names, messages, addresses, or other personal information into every monitoring system.
Use third-party challenges as a targeted layer
Some sites need an external risk service or challenge. Google documents reCAPTCHA v3 as a score-based approach that lets a site choose an action, such as additional verification, moderation, or throttling, based on the interaction context. That is different from a universal pass/fail guarantee. The service still requires server-side verification, and its external script, data handling, performance, accessibility, and consent implications need review.
Do not add a challenge to every form by default. Consider it when the endpoint is being abused, the value of a false acceptance is high, or other controls are not sufficient. If you use a score, define what the score changes. For example, lower-confidence requests might enter review rather than being deleted. Avoid making a score the only record of why a request was accepted or blocked.
Also test the challenge as part of the real page. Google’s documentation notes that reCAPTCHA can be loaded asynchronously, but the page must wait until the library is ready before calling it. A race condition can make the submit button fail even when the visitor has done everything correctly.
Protect the user experience while blocking abuse
Security controls are part of the form experience. They should not create a puzzle that only some visitors can complete.
- Keep visible labels, instructions, and required-field indicators clear.
- Make every field and control keyboard accessible.
- Keep entered values when validation fails so a visitor does not have to start again.
- Place a concise error summary where it can be found, then connect each error to its field.
- Explain what the visitor should do next without disclosing detection rules.
- Offer a contact alternative when a high-value workflow cannot be completed.
- Test the form with zoom, mobile keyboards, screen readers, slow connections, and scripting disabled where the workflow supports it.
The W3C Forms Tutorial recommends clear labels, instructions, validation, success and error notifications, and logical multi-page progress. These are not separate from spam prevention. A form that quietly rejects a legitimate visitor is a data-quality problem and a conversion problem at the same time.
Check the handoffs after the form accepts a request
Spam prevention is not complete when the browser shows a thank-you message. Confirm that:
- The stored record has the expected status and a stable identifier.
- Only accepted records trigger CRM creation, email automation, or other side effects.
- Review items remain excluded from automatic follow-up until approval.
- Analytics distinguishes a submitted form from an accepted, rejected, and reviewed request.
- Notifications contain enough context to act without duplicating private form data unnecessarily.
- Rate-limit and provider failures produce an observable error path.
- Retries do not create duplicate records or duplicate notifications.
Run these checks with test submissions that represent a normal visitor, a missing required value, a honeypot hit, a burst of requests, a failed risk-service response, and a request that enters review. Verify both the visible response and the downstream record. A green browser message alone does not prove that the workflow is correct.
Review the controls as the threat changes
Spam patterns change. Review the form’s rejection and quarantine categories on a schedule, looking for false positives, repeated sources, sudden volume changes, and messages that should have been routed to review. Adjust thresholds based on observed behavior, not on a vendor default that nobody can explain.
Keep an inventory of the form endpoint, owner, validation rules, third-party services, data fields, retention period, downstream destinations, and test cases. That inventory makes a future redesign or platform change much safer because the anti-spam workflow is documented as part of the site, not hidden inside a plugin setting.
Build a form that is difficult to abuse and easy to recover
Good form protection is layered and reviewable. Validate on the server, add low-friction signals, limit repeated requests, quarantine uncertainty, and use a challenge only when the evidence supports it. Then test the accessible user experience and every downstream handoff.
DigitalWerks can help review a website form, identify where spam controls are blocking real people or missing abusive traffic, and build a testable workflow across WordPress, notifications, analytics, CRM systems, and automation. Talk with DigitalWerks about a form and data-collection review.
Sources: W3C Forms Tutorial; W3C User Notification guidance; Google reCAPTCHA Developer Guide; Google reCAPTCHA loading guidance.